
Overview
OpenKey is a self-hosted, end-to-end encrypted password manager. Clients encrypt vault data before it leaves the device. The optional sync server stores ciphertext only — master passwords and plaintext vault keys never leave the client.
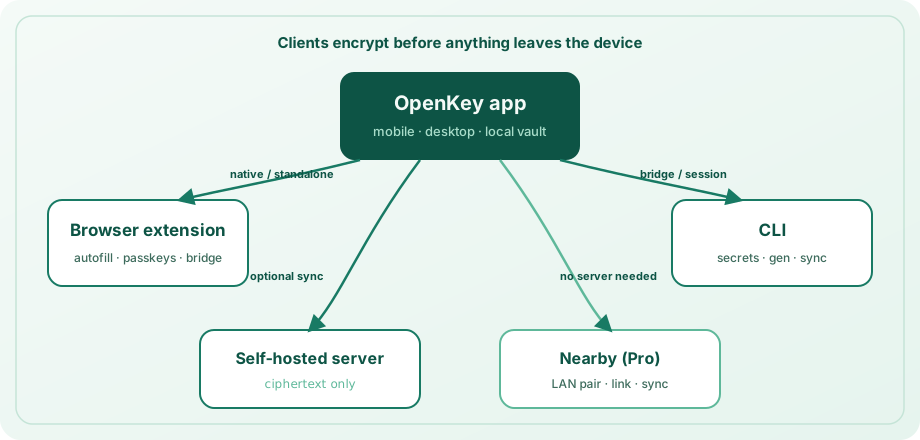
What you get
- Local encrypted vault (collections, logins, cards, crypto wallets, developer secrets)
- Optional sync across devices through your own server or Nearby LAN pairing (Pro)
- Browser extension with autofill, fill shortcut, and passkeys
- Mobile / desktop app and developer CLI
- Organizations, shared collections, and item shares — still ciphertext on the server
Zero-knowledge model
- The client derives keys from your master password with Argon2id.
- An
auth_hashauthenticates you to the server without revealing the master password. - Vault contents stay encrypted with a vault key that the server never sees in plaintext.
- Names, payloads, attachments, org names, and share payloads are opaque ciphertext at rest on the server.
Open packages
| Package | Role |
|---|---|
openkey_server | FastAPI zero-knowledge sync API + PostgreSQL |
openkey_extension | MV3 browser extension (Chrome / Firefox) |
openkey_cli | Developer CLI (secrets, password gen, sync) |
The mobile and desktop OpenKey app is a proprietary official client of this protocol. See Download, Using the app, Nearby, Browser extension, Packages, Server setup, FAQ, Changelog, and Quick start. Protocol details: OpenSelfHosting/OpenKey spec.